
Trail of Bits Open-Sources 30 Claude Code Plugins for Hunting Real Vulnerabilities
Trail of Bits published an open marketplace of 35+ Claude Code plugins that wire specialized security workflows directly into AI coding sessions.
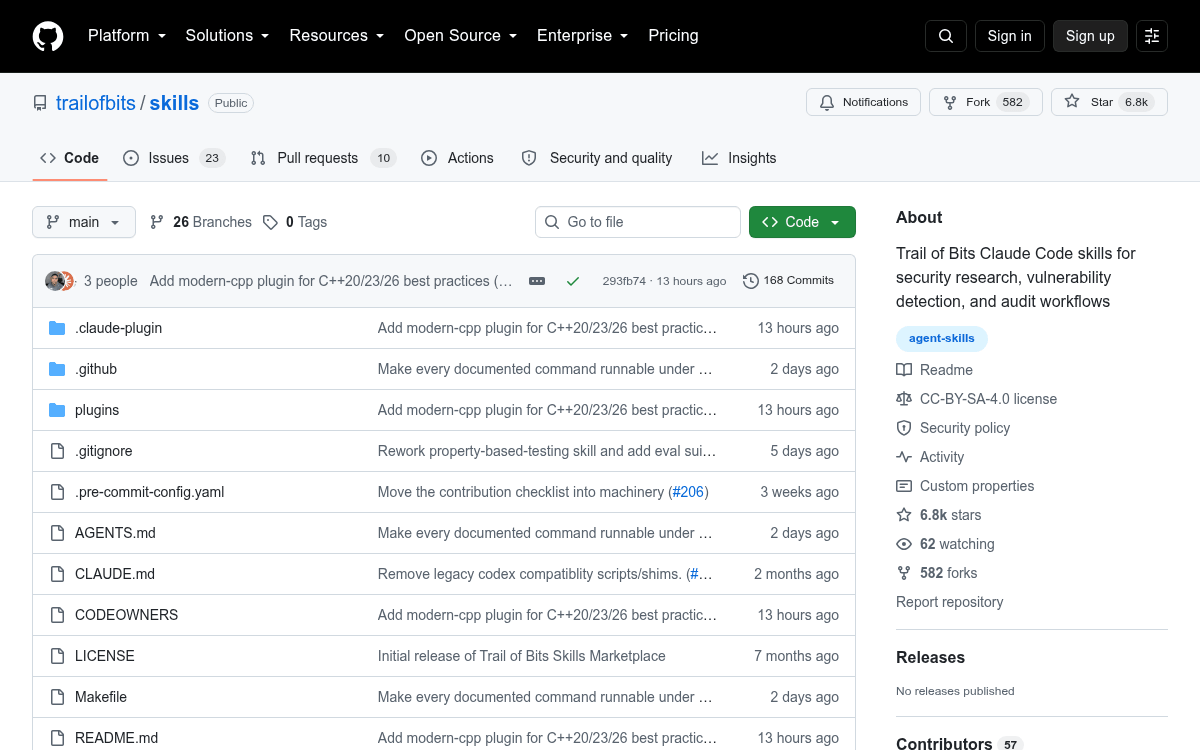
Takeaways
- Trail of Bits released an open Claude Code marketplace with 35+ security-focused plugins.
- Install via
/plugin marketplace add trailofbits/skills; also works with Codex CLI. - Covers smart contracts, C/C++ review, cryptography, YARA, Semgrep, and CI/CD auditing.
- Already credited with a real bug: a timing side-channel in ML-DSA signing.
- Includes
agentic-actions-auditorfor prompt injection risks in AI-driven GitHub workflows. - Free under CC-BY-SA-4.0; 5,000+ stars and 33 contributors on the repo.
Security firm Trail of Bits has open-sourced a large collection of Claude Code plugins aimed squarely at vulnerability hunting, code auditing, and cryptographic verification. The skills marketplace bundles more than thirty plugins covering everything from smart contract auditing to YARA rule authoring, and it has already crossed 5,000 GitHub stars.
Skills are a lightweight way to extend agentic coding tools. Each one is a folder containing a SKILL.md file with instructions, plus any scripts or configuration the agent needs. As one summary puts it, each SKILL.md shows up to your agent as a callable tool, where the frontmatter says when to use it and the body says how. Trail of Bits is packaging its consulting playbooks into that format so an AI assistant can execute them on demand.
Getting it running
Installation is a one-liner inside Claude Code:
/plugin marketplace add trailofbits/skills
/plugin menu
The repo also ships a sidecar for OpenAI's Codex CLI through a .codex/skills/ tree, installable via a shell script in the repo. Everything is released under Creative Commons Attribution-ShareAlike 4.0, so it is free to use and modify with attribution.
What's in the box
The plugins are organized into categories that mirror how a security consultancy divides its work. A few highlights worth knowing about:
- building-secure-contracts, a smart contract toolkit with vulnerability scanners for 6 blockchains and 5 development guideline assistants, based on Trail of Bits' internal framework of the same name.
- c-review runs comprehensive C/C++ security review for memory corruption, integer overflows, race conditions, and platform-specific vulnerabilities, using clustered parallel workers and emitting SARIF output for downstream tooling.